Link copied!
Regulation
Curaçao tries to scrub leaked licensing data from the internet, with mixed results so far
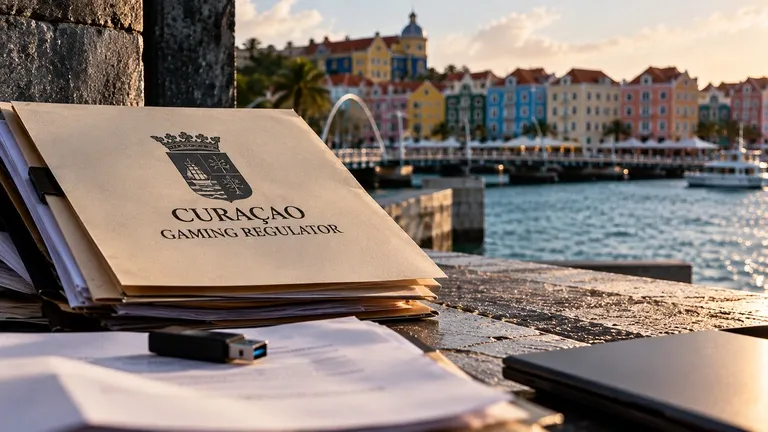
Curaçao’s gaming regulator has filed complaints in three countries and hired specialist firms to remove leaked licensing data from the internet, but one takedown attempt already failed when the archive simply reappeared on a new domain.
Complaints filed, removal already proving hard
Curaçao’s gaming regulator has filed formal complaints with authorities in Curaçao, Germany, and the Netherlands over what it calls unlawfully obtained data, and hired specialist firms to try to get the leaked material taken down from wherever it’s been republished. According to Curaçao Chronicle, the CGA is also weighing legal action against Lilith Wittmann, the security researcher behind the original breach, though it hasn’t specified whether that means a civil suit or which jurisdiction it would file in. An independent cybersecurity investigation is separately underway to establish exactly how much was accessed and what the full fallout looks like.
Removal in practice has already run into trouble. After one hosting domain carrying the leaked archive got taken offline, the material simply reappeared on a different domain, curacaofiles.com, where it remains publicly accessible. That’s not a hypothetical risk the CGA is trying to get ahead of, it’s something that already happened once, which makes the regulator’s stated goal of limiting the data’s spread look considerably harder to pull off than the announcement itself suggests. No timeline for full removal, or even confirmation that full removal is achievable at all, has been given.
A permanent break from the old portal vendor
Alongside the cleanup effort, the CGA is cutting ties with the vendor behind its old licensing portal entirely. The breach itself ran from December 2025 through September 2026 before being discovered on September 17, and rather than patch the same system back together, the regulator decided to permanently end its relationship with the external provider that managed both the portal and its database. A temporary replacement system was slated to go live on October 19, though public confirmation that it’s fully operational and that security checks are complete hasn’t surfaced yet, and the page is currently accessible by invitation only rather than open to the public. The CGA says it’s separately building a fully in-house portal it will control directly going forward, cutting the external vendor out of the picture for good. Licenses issued under the old system stay valid regardless of which portal is running underneath them, the regulator has been explicit that shutting down the breached system doesn’t touch the legal status of licenses already granted.
“
“One failed takedown that sends the archive straight to a new domain says more about what’s actually possible here than any press release does.”

Related tags


Share
SUBSCRIBE TO OUR PRIVATE CASES AND USEFUL TIPS
Subscribe to our newsletter, get only exclusive content and weekly digests, no any spam!
By providing my email, I accept the Privacy Policy.